Defending A Client with TigerTrax Investigative Services

Rounding out this week of TigerTrax™ blog posts, I wanted to discuss a particular case where we used our investigative social media and forensics capabilities to defend a professional sports client who was being accused of some illicit behavior. The case is a fairly powerful example of how TigerTrax can be used for reputational defense.

In this incident, the player was approached online by a young lady. This young lady began following the player on many social media networks, and the player’s software automatically followed/friended back the young lady, just as it does for all of the player’s followers on the social media networks. Over the next few weeks, the young lady in question began several conversations with the player. They would begin innocent enough, but would then begin to be filled with innuendo and inappropriate overtones. The player responded to the conversations, but remained in line with expected conversations that you would want a player to have with fans. The player, at no time, responded to any of the innuendo or more sexual content.

Later, the young lady began to edit the player’s content, posting it to other social networks and bragging about it to her high school friends. Eventually, her parents were informed, and confronted the young lady. The young lady told a story to her parents ~ a story that involved the player initiating the contact and being the one who was pursuing inappropriate overtones. The parents, naturally enraged, contacted the team and the player to discuss the situation. MSI was retained by the team to investigate prior to the meeting and provided with a printed version of what the young lady asserted were the details of the conversation online.

MSI leveraged the power of TigerTrax to gather the social media content relevant to the engagement. We captured both sides of the conversations, and to our amazement, we discovered that the young lady had edited the content to fit her tale. Many of the posts in her printed version of the conversation were heavily edited. Most of the posts made by her were deleted from her version (and in some cases deleted by her from the social media sites, but cached in TigerTrax archives and the search engines). Recreating the entire timeline and assembling the real content was done by the MSI analysts, and in the end, the factual stream of data was presented to the team. Once the parents and the young lady were provided with the copies of the report at the meeting, the young lady admitted her fabrication and came clean with the whole story. The parents apologized and the team and player expressed their understanding and completed the incident with their reputations intact.

MSI was proud to be able to help a client defend their reputation. We believe these capabilities will be a powerful addition to many professional sports teams, talent agencies and corporations who are seeking to protect their reputational integrity and remain vigilant against online behaviors that could damage their brand. To learn more about TigerTrax and the services surrounding it, please contact your account executive or reach out to me via Twitter (@lbhuston). We look forward to working with you.
TigerTrax Monitoring vs Professional Sports & Business

J0289377

By now, you may have heard about our new TigerTrax™ powered services. We formally announced them this week and the interest in them has been very high. Today, I wanted to provide a bit more context to the last year or so, especially around a particular use case for TigerTrax that is pretty unique and intriguing.

We originally developed the TigerTrax platform to super charge our threat intelligence activities against real bad guys in the world. It grew out of our need to better manage and explore the vast amounts of data we get from the HoneyPoint Internet Threat Monitoring Environment (HITME), but even as we leveraged it against cyber-crime, other use cases quickly emerged.

One of these use cases was developed by engaging directly with an NFL team. The team worked with us over a number of months as we tweaked out the capabilities of the system and adapted it to more of a social focus than a crime focus for their needs. Today, the system provides ongoing monitoring of a number of social media sites and their content, continually providing for both positive examples of expected behavior, as well as identifying violations of the player code of conduct. With all of the press and public media attention to some high profile examples of athlete misconduct, the teams are now taking this very seriously.

MSI has developed TigerTrax into a modular platform that easily scales to monitoring all of the player, cheerleader, coaching, back-office and ownership staff against the code of conduct. The social media content is gathered in near real time, and an analytics engine provides advanced techniques to flagging potential behavioral issues. The system is also continually adapted to new forms of behavior, shifting social issues (bullying, homophobic and racial issues, etc.) and the evolving concerns of the team management. Combining the TigerTrax technology with a team of deeply skilled human analysts, strong player skill development expertise and social media education focused on personal branding and social leadership was a natural fit for the evangelical approaches that MSI has practiced for more than 20 years in our information security engagements.

In addition, one of the key differentiators of TigerTrax, is not just the analysis of the key parties’ (players, cheerleaders, coaches, etc.) content, but also the global content from the social media sphere around specific events and actors. Using this crowd-sourced sensor approach, we have been able to identify misbehaviors and code of conduct violations, simply by capturing the data and correlating/validating it from observers in the public. The same techniques have also allowed us to use the public data to defend players and other parties against grossly exaggerated or completely false accusations against their character. Indeed, for some players, TigerTrax has made an excellent tool in DEFENDING their reputations!

Over the last few years, we have taken the initial platform developed for threat intelligence against cyber-crime, and adapted it to a variety of professional sports, business applications, investigative and forensic activities. We have expanded the platform beyond simple keyword analytics and are beginning to actuate on sentiment, data flow anomalies and deeper content analytical problem solving. In the years to come, we view TigerTrax as a very capable core business empowerment platform for MSI, just as impactful as HoneyPoint has been since 2006. We are still developing use cases for TigerTrax and the service offerings it has empowered for our clients. If you have a potential new use case that you would like to discuss, or if you would like to hear more about reputational threat intelligence and monitoring, please give us a call.

MSI is also seeking a handful of key business partners interested in helping us grow the TigerTrax platform adoption by bringing these unique capabilities to their clients, or by adapting the capabilities into new service offerings. If your business has an idea for how to leverage the TigerTrax capabilities, give us a call. We will be happy to explore new solutions with you.

As always, thanks for reading and thanks for partnering with MSI!

MSI Announces TigerTrax Reputational Threat Services

TigerTrax™ is MSI’s proprietary platform for gathering and analyzing data from the social media sphere and the overall web. This sophisticated platform, originally developed for threat intelligence purposes, provides the team with a unique capability to rapidly and effectively monitor the world’s data streams for potential points of interest.


The uses of the capability include social media code of conduct monitoring, rapid “deep dive” content gathering and analysis, social media investigations & forensics, organizational monitoring/research/profiling and, of course, threat intelligence.


The system is modular in nature, which allows MSI to create a number of “on demand” and managed services around the platform. Today the platform is in use in some of the following ways:

  • Sports teams are using the services to monitor professional athletes for potential code of conduct and brand damaging behaviors
  • Sports teams are also using the forensics aspects of the service to help defend their athletes against false behavior-related claims
  • Additionally, sports teams have begun to use the service for reputational analysis around trades/drafts, etc.
  • Financial organizations are using the service to monitor social media content for signs of illicit behavior or potential legal/regulatory violations
  • Talent agencies are monitoring their talent pools for content that could impact their public brands
  • Law firms are leveraging the service to identify potential issues with a given case and for investigation/forensics
  • Companies have begun to depend on the service for content monitoring during mergers and acquisitions activities, including quiet period monitoring and pre-offer intelligence
  • Many, many more uses of the platform are emerging every day

 If your organization has a need to understand or monitor the social media sphere and deep web content around an issue, a reputational concern or a code of conduct, discuss how TigerTrax from MSI can help meet your needs with an account executive today.


At a glance call outs:

  • Social media investigation/forensics and monitoring services
  • Customized to your specific concerns or code of conduct
  • Can provide deep dive background information or ongoing monitoring
  • Actionable reporting with direct support from MSI Analysts
  • Several pricing plans available

Key Differentiators:

  • Powerful, customizable, proprietary platform
  • Automated engines, bleeding edge analytics & human analysts to provide valuable insights
  • No web portal to learn or analytics software to configure and maintain
  • No heavy lifting on customers, MSI does the hard work, you get the results
  • Flexible reporting to meet your business needs

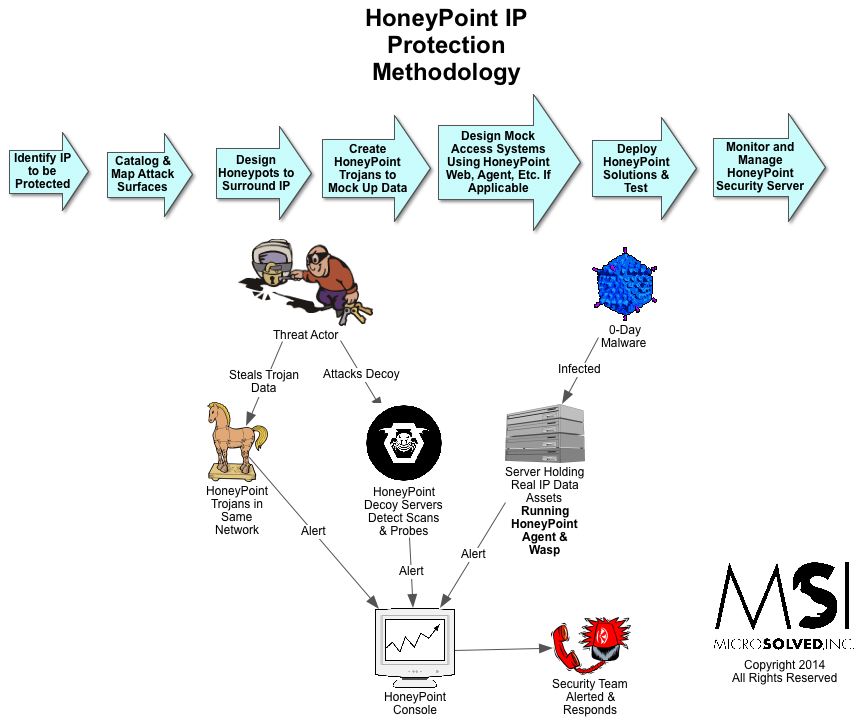
HoneyPoint IP Protection Methodology

Here’s another use case scenario for HoneyPoint Security Server. This time, we show the methodology we use to scope a HoneyPoint implementation around protecting a specific set of Intellectual Property (IP). 

If you would like an in-depth discussion of our process or our capability, please feel free to reach out to us and schedule a call with our team. No commitment and no hard sale, guaranteed.

If the graphic below is blurry on your device, you can download a PDF version here.

HP_IPProtection

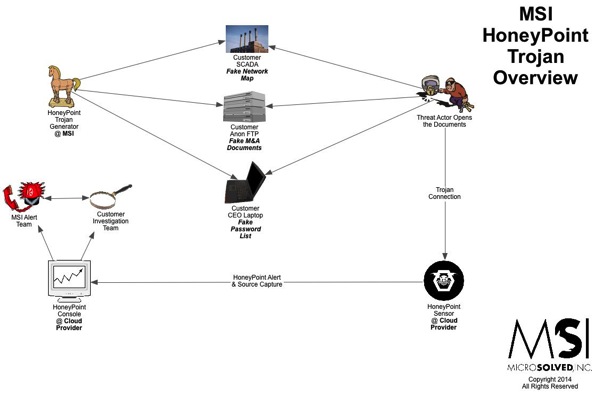
HoneyPoint Trojans Overview

Here’s another quick overview graphic of how HoneyPoint Trojans work. We have been using these techniques since around 2008 and they are very powerful. 

We have incorporated them into phishing exercises, piracy studies, incident response, intrusion detection, intelligence gathering, marketing analysis and even privacy research. To hear more about HoneyPoint Trojans, give us a call.

If the graphic below is blurry on your device, you can download a PDF version here.

HPTrojanOverview

Touchdown Task for January: Audit Your News Feeds

This month, our suggested Touchdown Task is for the security team to do an “audit” of their news/RSS feeds and the other mechanisms by which you get advisories, patch and upgrade alerts, breakout information and details about emerging threats.

Since RSS feeds and account names and such can change, it’s a good idea to review these sources occasionally. Are the feeds you depend on timely and accurate? Have you added new technology to your organization since you last reviewed your advisory feeds? Maybe you might need to add a vendor or regulator feed.

Have a discussion with all of your team members and understand who monitors what. Make sure you have good cross communication, but aren’t struggling with a lot of duplicated efforts.

Once you get your news and threat feeds in order, trace how the information is shared and make sure it is getting to the system and network admins who might need it. Do you have the right people getting the right information? If not, adjust. 

Most teams can do this review in less than an hour. So focus, communicate and create a robust way to handle the flow of information.

As always, thanks for reading and stay safe out there! 

Blast From the Past: D-Link Probes in the HITME

We got a few scans for an old D-Link router vulnerability that dates back to 2009. It’s interesting to me how long scanning signatures live in online malware and scanning tools. This has lived for quite a while. 

Here are the catches from a HoneyPoint Personal Edition I have deployed at home and exposed to the Internet. Mostly, this is just to give folks looking at the scans in their logs an idea of what is going on. (xxx) replaces the IP address… 

2013-10-02 02:46:13 – HoneyPoint received a probe from 71.103.222.99 on port 80 Input: GET /HNAP1/ HTTP/1.1 Host: xxxx User-Agent: Mozilla/4.0 (compatible; MSIE 6.0; Win32) WebWasher 3.0 Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8 Accept-Language: en-US,en;q=0.5 Accept-Encoding: gzip, deflate Referer: http://xxxx/ Authorization: Basic YWRtaW46dWA+NXhZQlU1d2VR Connection: keep-alive

2013-10-02 03:22:13 – HoneyPoint received a probe from 71.224.194.47 on port 80 Input: GET /HNAP1/ HTTP/1.1 Host: xxxx User-Agent: Opera/6.x (Linux 2.4.8-26mdk i686; U) [en] Accept: text/html,application/xhtml+xml,application/xml;q=0.9,*/*;q=0.8 Accept-Language: en-US,en;q=0.5 Accept-Encoding: gzip, deflate Referer: http://xxxx/ Authorization: Basic YWRtaW46InkwYi4qMF5wL05G Connection: keep-alive

This probe is often associated with vulnerable D-Link routers, usually older ones, those made between 2006 and mid-2010. The original release and proof of concept exploit tool is here. The scan has also been embedded into several scanning tools and a couple of pieces of malware, so it continues to thrive.

Obviously, if you are using these older D-Link routers at home or in a business, make sure they are updated to the latest firmware, and they may still be vulnerable, depending on their age. You should replace older routers with this vulnerability if they can not be upgraded. 

The proof of concept exploit also contains an excellent doc that explains the HNAP protocol in detail. Give it a read. It’s dated, but remains very interesting.

PS – As an aside, I also ran the exploit through VirusTotal to see what kind of detection rate it gets. 0% was the answer, at least for that basic exploit PoC. 

Scanning Targets for PHP My Admin Scans

Another quick update today. This time an updated list of the common locations where web scanning tools in the wild are checking for PHPMyAdmin. As you know, this is one of the most common attacks against PHP sites. You should check to make sure your site does not have a real file in these locations or that if it exists, it is properly secured.

The scanners are checking the following locations these days:

//phpMyAdmin/scripts/setup.php
//phpmyadmin/scripts/setup.php
/Admin/phpMyAdmin/scripts/setup.php
/Admin/phpmyadmin/scripts/setup.php
/_PHPMYADMIN/scripts/setup.php
/_pHpMyAdMiN/scripts/setup.php
/_phpMyAdmin/scripts/setup.php
/_phpmyadmin/scripts/setup.php
/admin/phpmyadmin/scripts/setup.php
/administrator/components/com_joommyadmin/phpmyadmin/scripts/setup.php
/apache-default/phpmyadmin/scripts/setup.php
/blog/phpmyadmin/scripts/setup.php
/cpanelphpmyadmin/scripts/setup.php
/cpphpmyadmin/scripts/setup.php
/forum/phpmyadmin/scripts/setup.php
/php/phpmyadmin/scripts/setup.php
/phpMyAdmin-2.10.0.0/scripts/setup.php
/phpMyAdmin-2.10.0.1/scripts/setup.php
/phpMyAdmin-2.10.0.2/scripts/setup.php
/phpMyAdmin-2.10.0/scripts/setup.php
/phpMyAdmin-2.10.1.0/scripts/setup.php
/phpMyAdmin-2.10.2.0/scripts/setup.php
/phpMyAdmin-2.11.0.0/scripts/setup.php
/phpMyAdmin-2.11.1-all-languages/scripts/setup.php
/phpMyAdmin-2.11.1.0/scripts/setup.php
/phpMyAdmin-2.11.1.1/scripts/setup.php
/phpMyAdmin-2.11.1.2/scripts/setup.php
/phpMyAdmin-2.5.5-pl1/index.php
/phpMyAdmin-2.5.5/index.php
/phpMyAdmin-2.6.1-pl2/scripts/setup.php
/phpMyAdmin-2.6.1-pl3/scripts/setup.php
/phpMyAdmin-2.6.4-pl3/scripts/setup.php
/phpMyAdmin-2.6.4-pl4/scripts/setup.php
/phpMyAdmin-2.6.4-rc1/scripts/setup.php
/phpMyAdmin-2.6.5/scripts/setup.php
/phpMyAdmin-2.6.6/scripts/setup.php
/phpMyAdmin-2.6.9/scripts/setup.php
/phpMyAdmin-2.7.0-beta1/scripts/setup.php
/phpMyAdmin-2.7.0-pl1/scripts/setup.php
/phpMyAdmin-2.7.0-pl2/scripts/setup.php
/phpMyAdmin-2.7.0-rc1/scripts/setup.php
/phpMyAdmin-2.7.5/scripts/setup.php
/phpMyAdmin-2.7.6/scripts/setup.php
/phpMyAdmin-2.7.7/scripts/setup.php
/phpMyAdmin-2.8.2.3/scripts/setup.php
/phpMyAdmin-2.8.2/scripts/setup.php
/phpMyAdmin-2.8.3/scripts/setup.php
/phpMyAdmin-2.8.4/scripts/setup.php
/phpMyAdmin-2.8.5/scripts/setup.php
/phpMyAdmin-2.8.6/scripts/setup.php
/phpMyAdmin-2.8.7/scripts/setup.php
/phpMyAdmin-2.8.8/scripts/setup.php
/phpMyAdmin-2.8.9/scripts/setup.php
/phpMyAdmin-2.9.0-rc1/scripts/setup.php
/phpMyAdmin-2.9.0.1/scripts/setup.php
/phpMyAdmin-2.9.0.2/scripts/setup.php
/phpMyAdmin-2.9.0/scripts/setup.php
/phpMyAdmin-2.9.1/scripts/setup.php
/phpMyAdmin-2.9.2/scripts/setup.php
/phpMyAdmin-2/
/phpMyAdmin-2/scripts/setup.php
/phpMyAdmin-3.0.0-rc1-english/scripts/setup.php
/phpMyAdmin-3.0.0.0-all-languages/scripts/setup.php
/phpMyAdmin-3.0.1.0-english/scripts/setup.php
/phpMyAdmin-3.0.1.0/scripts/setup.php
/phpMyAdmin-3.0.1.1/scripts/setup.php
/phpMyAdmin-3.1.0.0-english/scripts/setup.php
/phpMyAdmin-3.1.0.0/scripts/setup.php
/phpMyAdmin-3.1.1.0-all-languages/scripts/setup.php
/phpMyAdmin-3.1.2.0-all-languages/scripts/setup.php
/phpMyAdmin-3.1.2.0-english/scripts/setup.php
/phpMyAdmin-3.1.2.0/scripts/setup.php
/phpMyAdmin-3.4.3.1/scripts/setup.php
/phpMyAdmin/
/phpMyAdmin/scripts/setup.php
/phpMyAdmin/translators.html
/phpMyAdmin2/
/phpMyAdmin2/scripts/setup.php
/phpMyAdmin3/scripts/setup.php
/phpmyadmin/
/phpmyadmin/scripts/setup.php
/phpmyadmin1/scripts/setup.php
/phpmyadmin2/
/phpmyadmin2/scripts/setup.php
/phpmyadmin3/scripts/setup.php
/typo3/phpmyadmin/scripts/setup.php
/web/phpMyAdmin/scripts/setup.php
/xampp/phpmyadmin/scripts/setup.php
<title>phpMyAdmin

Telnet Passwords Used In Brute Force Attacks

Just a quick post today, but I wanted to give you some insight into the Telnet scans we have been seeing lately. Here are the passwords that have been used to target logins on port 23 on one of our HITME sensors in the United States. This particular system emulates a login, and the probes appear to be automated. We saw no evidence of any manual probes on this sensor in the last month that targeted telnet.

The passwords used in brute force attacks on telnet (used against the usual root/admin/etc users…): 

default
1234
220
428
436
Admin
D-Link
admin
cobr4
dreambox
echo
enable
home-modem
l
password
private
public
root
sh
user

Keep a careful eye on any systems with Telnet exposed to the Internet. They are a common attraction point to attackers.

China’s Report on US Military Cyber Troop Strength

(紅龍) Red Dragon’s statement: If you think you are paying too much for cyber threat intelligence and your current provider DID NOT SHOW this Chinese article to you…then you have paid too much for the incorrect type of Chinese Cyber Threat Intelligence…

Contact the Red Dragon (紅龍) @ MicroSolved, save money, stay better informed – find a capable cyber intelligence authority for less, much less….

whagestad@microsolved.com

謝謝您

紅龍

People’s Republic of China Report: U.S. network warfare unit’s equivalent to 7 over 8 million people equal to the 101st Airborne Division

At 08:49 on August 15, 2013 Source: Phoenix

Core Tip : According to Sing Tao Global Network reported that the U.S. share of global 29% of the number of hackers, the U.S. military about 3000-5000 information warfare experts, and 50000-70000 cyberwar soldiers, together with the original electronic warfare officer , the U.S. network warfare units should have eighty-eight thousand seven hundred people, the scale is equivalent to seven 101st Airborne Division, which will burden future wars weakened the enemy four into combat missions.

Phoenix August 14 “military observation room”, the following is the text Record:

Commentary: Snowdon event causes a foreign media speculation, in fact, the United States first established the largest network warfare units, the development of the world’s most advanced network warfare equipment, and bringing it to actual combat. Recently, the Sing Tao Global Network reported that the U.S. share of global 29% of the number of hackers, the U.S. military about 3000-5000 information warfare experts, and 50000-70000 cyberwar soldiers, together with the original electronic warfare officer, U.S. Army network warfare units should have eighty-eight thousand seven hundred people, the scale is equivalent to seven 101st Airborne Division, which will burden future wars to weaken the enemy four combat missions.

U.S. network army of four thousand people, the world’s top computer experts and hackers, including the CIA, NSA, FBI and other sector experts, all members of the average IQ of 140 or more, known as 140 troops from American four-star general Alexander lasted eight single-handedly built his independent command of the Tenth Fleet, including the Navy, the Air Force 24th Air Force and the Army Second Army, responsible for the training of the academic elite spy technology centers, as well as specialized eavesdropping embassies around the world special data collection center, the United States is being set up forty network security forces, including 13 as offensive forces, the main development network warfare weapons, another 27 troops mainly to protect DoD computer systems and data, all 40 teams will branch to be completed before the autumn of 2015.

“Military observation room” program broadcast in the Phoenix Chinese Channel ] [Program Area

Moderator: Dong Jiayao Moderator Zone]

First time: (Wednesday) 21:50-22:30

Playback time: (Thursday) 04:10-04:50,15:15-15:55

Statement : where marked “Phoenix” sources of work (text, audio, video), without the Phoenix authorization, any media, and individuals shall not be reproduced, link, posted or otherwise use; already authorized in writing by the webmaster at use must be marked “Source: Phoenix.” Violate the above statement, Ben Wang will pursue its legal responsibilities.

 美國網路戰部隊逾8萬人 相當於7個101空降師2013年08月15日 08:49

來源:鳳凰衛視

核心提示:據星島環球網報道,美國駭客數量佔全球29%,美軍約有三千到五千名資訊戰專家,及五萬到七萬名網路戰兵,加上原有的電子戰人員,美軍網路戰部隊應該有八萬八千七百人,這個規模相當於七個101空降師,它在未來戰爭將負擔削弱敵人四成戰鬥力的任務。

鳳凰衛視8月14日《軍情觀察室》,以下為文字實錄:

解說:斯諾登事件引起中外媒體一輪炒作,其實美國最早建立規模最大的網路戰部隊,發展了世界最先進的網路戰裝備,並將其推向實戰。近日,星島環球網報道,美國駭客數量佔全球29%,美軍約有三千到五千名資訊戰專家,及五萬到七萬名網路戰兵,加上原有的電子戰人員,美軍網路戰部隊應該有八萬八千七百人,這個規模相當於七個101空降師,它在未來戰爭將負擔削弱敵人四成戰鬥力的任務。

美國網軍達四千人,由世界頂級電腦專家和駭客組成,包括中央情報局、國家安全局、聯邦調查局以及其他部門的專家,所有成員平均智商在140以上,稱為140部隊,由美國四星上將亞歷山大歷時八年一手打造,他獨立指揮權包括海軍第十艦隊,空軍第24航空隊以及陸軍第二軍,負責培訓間諜技術的學術精英中心,以及專門竊聽世界各國大使館的特殊數據收集中心,美國正在組建四十支網路安全部隊,其中13支為進攻性部隊,主要開發網路戰武器,另外27支部隊主要保護國防部的電腦系統和資料,所有40支部隊將於2015年秋季前全部建成。

《軍情觀察室》節目在鳳凰衛視中文臺播出【節目專區】

http://big5.ifeng.com/gate/big5/phtv.ifeng.com/program/jqgcs/

主持人:董嘉耀【主持人專區】

首播時間:(週三)21:50-22:30

重播時間:(週四)04:10-04:50,15:15-15:55

聲明:凡註明“鳳凰網”來源之作品(文字、音頻、視頻),未經鳳凰網授權,任何媒體和個人不得轉載、鏈結、轉貼或以其他方式使用;已經本網書面授權的,在使用時必須註明“來源:鳳凰網”。違反上述聲明的,本網將追究其相關法律責任。

 http://big5.ifeng.com/gate/big5/phtv.ifeng.com/program/jqgcs/detail_2013_08/15/28642074_0.shtml